Walkthroughs · Illustrative, not client reports
Security work,
explained.
From a realistic attack to a flaw in your code. Explore how we test your defenses, applications, and infrastructure—and turn findings into a clear path to fix them.
Assessment walkthroughs
Inside an assessment.
The walkthroughs below illustrate our testing approach, not reproduced client reports. Client details remain confidential; no client metrics, timelines, or retest outcomes are published here.
Assessment walkthrough
Internal access paths and detection.
An assumed-breach assessment examines how a standard account could reach critical systems, and what evidence defenders would have along the way.
Read the walkthrough- Initial access
- Internal permissions
- Critical systems
Read the engagement summary for context and limitations.
Assessment walkthrough
Application portfolios and shared risk.
A coordinated web and mobile assessment examines authorization, source exposure, and security weaknesses shared across applications.
Read the walkthrough- Application scope
- Verified findings
- Prioritized fixes
Read the engagement summary for context and limitations.
Assessment walkthrough
File uploads and execution risk.
An upload assessment examines validation, storage, execution permissions, and access controls together. Explore the illustrated testing approach.
Read the walkthrough- File upload
- Server execution
- Access restrictions
Read the engagement summary for context and limitations.
Recorded investigations
Blockchain investigations,
with Web3 Forensia.
A separate collection of public on-chain investigations. Watch the Bitget, Bybit, and Coldcard wallet demos, then explore the addresses and evidence behind each case.
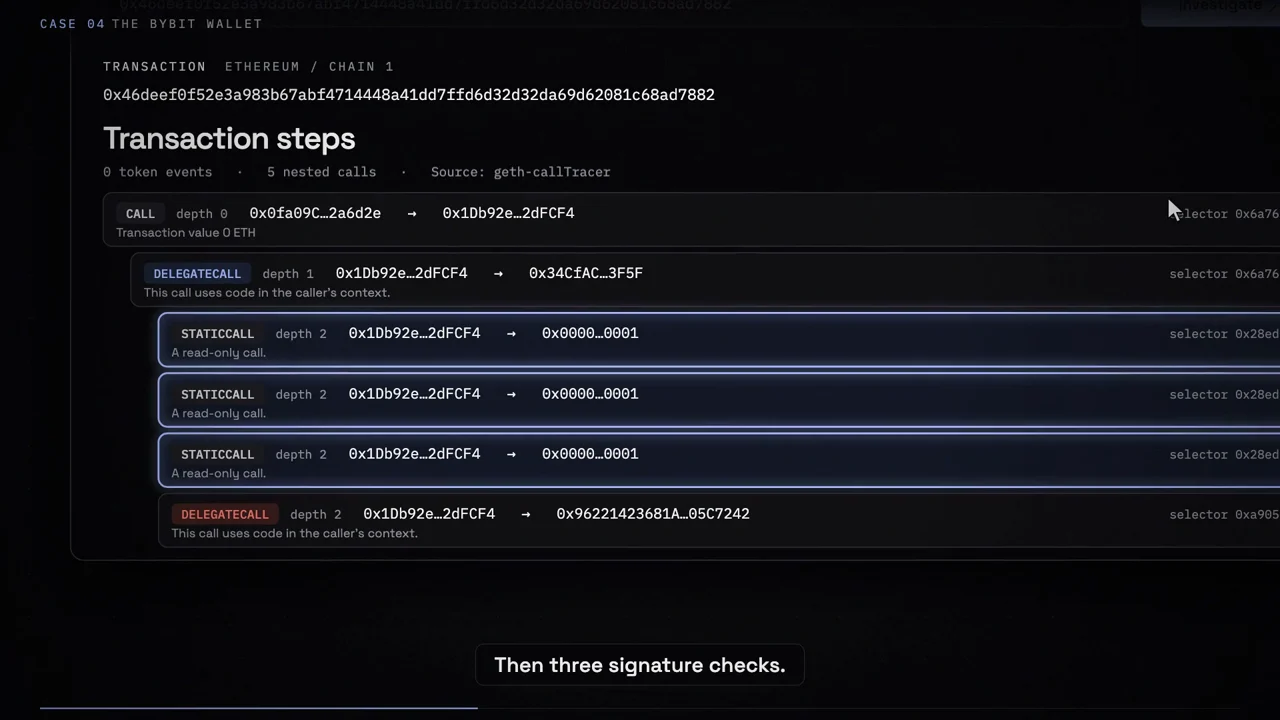 Watch the Bybit investigation · 1:24
Define your assessment.
Tell us about your systems and concerns. We’ll help define a practical scope.