Follow a request across an account boundary. Test the rules around private data, APIs and business workflows.
Explore application testing
ISO/IEC 27001:2022 certified company
Find the gaps.
Find the gaps.
Before attackers do.
Offensive security and penetration testing services for your applications, networks, and defenses. Verified findings. Clear priorities. Practical fixes.
From scope to a useful handoffOne request. A different outcome.1 / 4
Find
Start with the expected.
Account A asks for its own record. Establish what normal access looks like.
GET /accounts/A200 OKInspect the record
- Requested by
- account_A
- Returned owner
- account_A
Choose a step or play the sequence
Illustrative test · synthetic accounts · no live requests.
Company certification
ISO/IEC 27001:2022 certified.
Security is what we test.
It’s also how we operate.
500+ web application assessments personally completed by Abhimanyu Gupta
All industries welcome, with experience in pharmaceuticals, insurance, finance, travel, and AI-agent security.
Meet your security partnerCertified operators, not a badge on a shelf.
About the qualifications
The people who run your engagement hold the field’s hardest hands-on certifications, the kind earned by compromising real machines under exam conditions rather than by a multiple-choice test.
 OSCPOffensive Security Certified Professional
- eCPPTCertified Professional Penetration Tester
 OSCE3Offensive Security Certified Expert 3
 CISSPCertified Information Systems Security Professional
- EC-CouncilCertified Ethical Hacker and council programs
Four disciplines.
One clear next step.
Different systems need different questions. Explore the evidence each assessment looks for, then open its scope and deliverables.
Map exposed services, internal routes and identity boundaries. An open path is a question to investigate, not proof of compromise.
Explore network testingFollow an agreed attack objective through detection and response. Starting points, safeguards and exclusions are defined before testing.
Explore adversary simulationInspect sensitive code paths and the checks that enforce trust. Connect a finding to a practical change and a regression test.
Explore code reviewApplication securityIllustrative scope
A login is not a permission.
Follow a request across an account boundary. Test the rules around private data, APIs and business workflows.
- Web applications
- APIs
- Mobile apps
Network assessmentIllustrative scope
What can an entry point reach?
Map exposed services, internal routes and identity boundaries. An open path is a question to investigate, not proof of compromise.
- Networks
- Active Directory
- Cloud
Red teamingIllustrative scope
Would your defenses see the path?
Follow an agreed attack objective through detection and response. Starting points, safeguards and exclusions are defined before testing.
- Detection
- Response
- Objectives
Source code reviewIllustrative scope
Trace the decision back to the code.
Inspect sensitive code paths and the checks that enforce trust. Connect a finding to a practical change and a regression test.
- Code paths
- Dependencies
- Pipelines
A way to understand the assessment. Not a scan or a live finding.
From the right question
to a useful handoff.
The hero shows one illustrative authorization test. A real engagement starts with your environment, agreed scope and safeguards.
- 01
Agree the boundary.
Define systems, permissions, exclusions and stop-test triggers. Know what will be tested before the work begins.
Shape the scope → - 02
Make the evidence useful.
Manually validate findings. Connect reproducible evidence to business impact and practical remediation.
Explore assessment walkthroughs → - 03
Help the fix hold.
Hand over clear priorities. Retest scope and timing are agreed in your proposal, with limits documented.
Inspect the sample report →
For your team
Start with your situation.
You don’t need to know every security term to choose a useful next step. Find the path that fits your team.
See the tools.
Follow the work.
Six recorded walkthroughs. Choose a tool and press play to see how it works. The recordings are demonstrations, not live results.
checkYourDomainSec
Domain exposure, DNS and email security, explained in a recorded walkthrough.
The recording could not load. Try the recording download link below or reload the page.
Download this recording ↓Playback starts only when you choose. No sound or videos autoplay.
Recorded investigations
Three investigations,
on screen.
See how Web3 Forensia follows public activity, examines the evidence, and makes the limits clear. These are recorded product demonstrations, not client engagements.
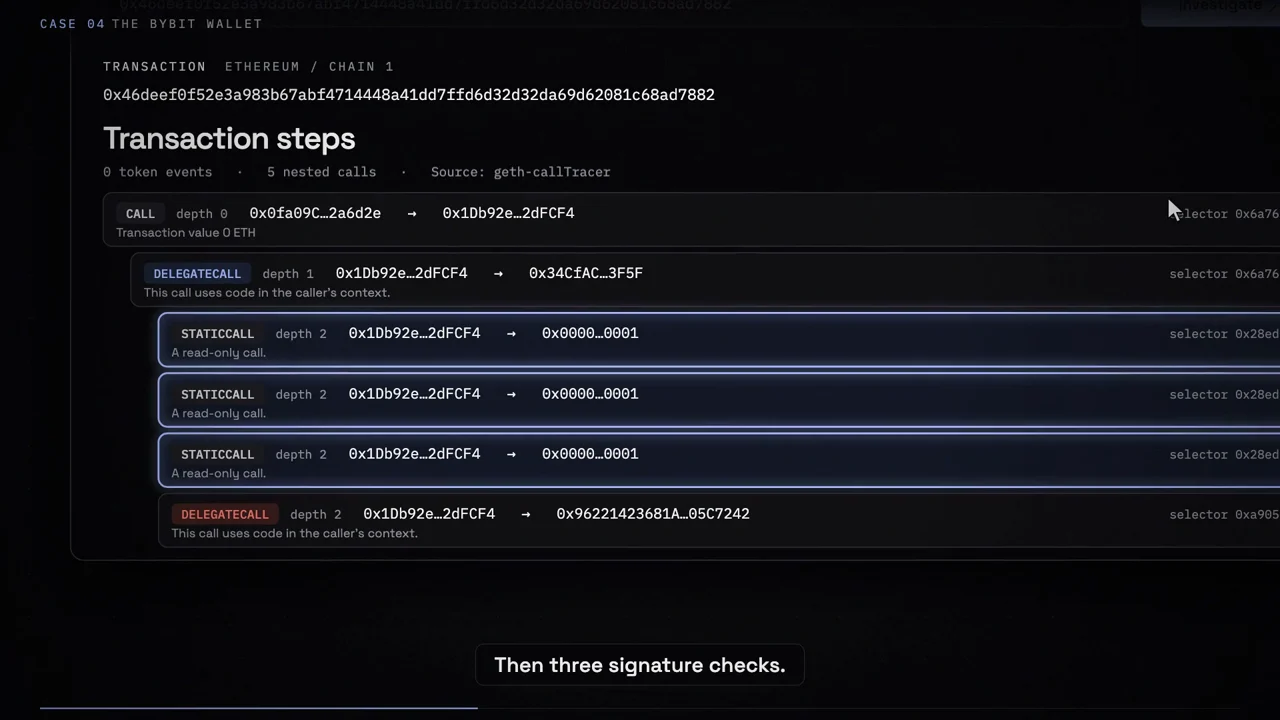
OVERWATCHCase film 01Recorded demo
1:24
Web3 Forensia walkthrough
Bybit investigation
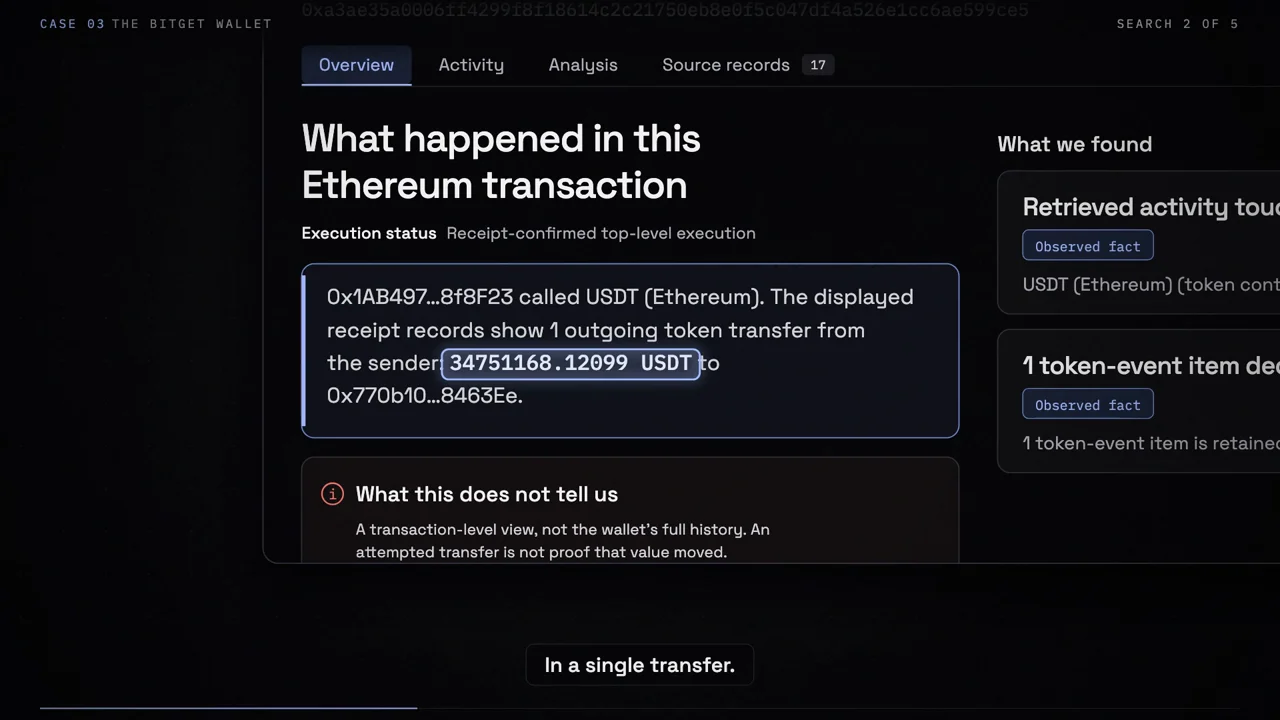
OVERWATCHCase film 02Recorded demo
1:51
Web3 Forensia walkthrough
Bitget investigation
OVERWATCHCase film 03Recorded demo
2:06
Web3 Forensia walkthrough
Coldcard wallet investigation
Bybit investigation
Explore the transaction and contract evidence shown in this Web3 Forensia walkthrough. Read the execution trace and contract context.
Distinguishes on-chain observations from sourced attribution. Recorded demonstration, not live data.
Open all three with addresses & artifacts
Service walkthroughs · illustrative, not client reports
Scope & what you receive
The right scope.
Evidence your team can use.
Security testing isn’t one-size-fits-all. Choose what you want to assess and see what shapes the engagement. Pricing is confirmed after scoping.
01What goes in
Application assessment
Scoped to your environment- What we test
- Authentication, access control, APIs, input handling, and business logic.
- What shapes the price
- Applications and endpoints, number of user roles, integrations, and testing depth.
- What to share
- Application URLs, test accounts for each role, API documentation, and your deadline.
- What you receive
- Verified findings, reproduction evidence, business impact, and practical remediation guidance. Retest scope and timing are agreed in your proposal.
Quoted after scopingScope, deliverables, and timeline agreed before testing.
Request my quote 02What comes out
A finding is only useful when someone can act on it. Explore what goes into the handoff, from reproduction steps to the retest result.
OverWatch Labs / AssessmentExample
AUTH-01 · Broken access control
One account can read another account’s record.
- Evidence
- Account A requests a synthetic record belonging to account B. The server returns its contents.
- Business impact
- An unrelated user could access private information across account boundaries.
GET /accounts/B → 200 OKReproducible. Prioritized. Actionable.01 / 03
Illustrative walkthrough, not a client report.
Explore case studiesNot sure where to start? Tell us what you’re building. We’ll help define the assessment.
Free tools
Five free tools. No sign-up.
Built for the work we do every week, and left open for everyone else. Four of the five run entirely in your browser, so the email you are suspicious about, the link you were sent, the token you found in a log and the file that arrived with it never leave your machine.
Understand the risk. Know the next step.
Explore practical security guides, from account boundaries to threat intelligence. No sales conversation required.
FAQ
Questions, answered.
Will testing break anything?
Testing is designed to minimize disruption, but no intrusive assessment is risk-free. We agree safeguards and stop-test triggers before testing. Rules of engagement, blast radius, and out-of-scope systems are all agreed before we start.
How long does an engagement take?
Most run one to four weeks depending on scope. You get a firm timeline after the scoping call, no open-ended clocks.
Is everything confidential?
Yes. Every engagement is covered by a mutual NDA, and findings are shared only with you.
Do you just run automated scanners?
No. Testing is hands-on. Tooling helps with coverage, but every finding is verified and exploited by hand.
Start with one conversation
See how you'd
be breached.
Tell us what you need. A senior operator replies within one business day. No sales pipeline, no bot.
Reach the founder directly